
Security baked in, not bolted on
Cloud adoption isn’t slowing down, and neither are the threats that come with it. What’s striking, though, is that more often than not, the root cause of security threats is seldom from sophisticated hackers, but from small mistakes: a misconfigured setting, a permission that was never scoped down, or an architectural shortcut taken under deadline pressure.
For a long time, the standard approach was to treat security as the last checkpoint before go-live, something you tested for, rather than something you built with – bolted in later rather than baked in from the start. The problem is that retrofitting security into a cloud environment that’s already running is slow, expensive, and rarely gets to the root of the issue. You end up patching symptoms while the underlying architecture stays fragile. The organisations that fare better are the ones that build security into their cloud foundations from the outset, rather than trying to bolt it on once things are already live.
What secure-by-design means in practice
At its core, secure-by-design means security is part of the architecture, the delivery pipeline, and day-to-day operations, rather than a separate workstream that runs alongside them. That includes strong identity controls, configurations that are defined and enforced consistently, automated checks built into the pipeline, ongoing monitoring, and, just as importantly, clear ownership of who’s responsible for what. Put those together and you get a cloud environment that’s harder to compromise, quicker to recover when something does go wrong, and better able to support growth without security becoming the thing that slows everyone down.
The trouble with reactive security
When security only gets a proper look right before deployment, teams tend to find problems at the worst possible time. Discovering a serious misconfiguration a week before launch leaves you with two bad options: push the release back, or ship it with a known gap and hope it doesn’t get exploited. Neither is a good place to be.
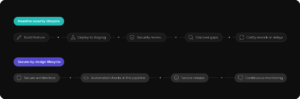
The difference compounds over time. As an organisation’s digital footprint grows, unresolved gaps multiply. Fixing an architectural flaw after the fact almost always costs more, in time and money, than getting it right in the first place. Reactive security doesn’t even deliver the trade-off it promises: it slows delivery down and still leaves real gaps in place.
Designing security into the architecture from day one
Good cloud security starts well before a workload ever touches production. A few principles tend to show up consistently in environments that hold up under pressure:
- Least privilege and limited access: The fundamental layer of protection where every component, service and user should operate strictly with only the permissions it needs and nothing more
- Network segmentation and workload isolation: Splitting environments into distinct zones limits how far an attack can move if one part is breached
- Zero-trust as a default: No user, device or service is trusted automatically, whether it sits inside the network perimeter or outside it
- A smaller attack surface: Closing unused ports, removing services nobody’s using, and switching off default admin endpoints that were never meant to stay open
Building security into the delivery pipeline
Security must scale at the same pace as feature delivery, and periodic manual audits simply can’t keep up with a modern release cadence. The more effective approach is to fold security checks directly into CI/CD: static and dynamic code analysis, dependency scanning, container inspection, so problems surface during the build itself rather than after release.
This is the “shift-left” idea in practice: catch issues earlier, fix them faster, and give engineering teams more confidence in what they’re shipping. It works best when it’s treated as part of normal quality assurance rather than a separate security gate bolted onto the end of the process.
Identity as the real perimeter
In a cloud-first world, identity does a lot of the work that network perimeters used to do. Getting it right matters more than most teams initially assume.
| Focus Area | Core principle | What it achieves |
| Identity verification | Continuous authentication, zero-trust | Limits the damage if credentials are compromised |
| Authorisation | Role-Based access control, least privilege | Removes unnecessary exposure and over-privileged accounts |
| Operational control | Enforced MFA, just-in-time access | Strengthens governance and make audits easier. |
A formal cloud security risk assessment is a useful way to surface identity weaknesses early, before infrastructure complexity makes them harder to untangle.
Monitoring is ongoing, not a milestone
Cloud security isn’t a project with an end date, instead, it’s a capability an organisation must keep exercising. That means real visibility across infrastructure, application logs and user activity, not just a dashboard that gets checked occasionally.
Good observability tooling helps teams catch anomalies, unauthorised access attempts, or subtle behavioural changes before they turn into full incidents. Paired with clear escalation paths and some degree of automated response, this is what keeps an environment resilient as threats continue to evolve. It’s also one of the areas where managed services earn their keep: sustained monitoring is hard to maintain in-house once a team’s attention is pulled toward feature work, which is part of why BBD builds it into its ongoing managed services rather than treating it as a one-time setup step.
BBD’s approach to cloud engineering is engineering-led: security is built into the architecture, the delivery automation, and the managed services that keep environments running afterward. The aim is to help organisations build cloud foundations that stay resilient and scalable as they grow, rather than needing to be re-secured every time they scale.
Combining solid governance with real observability and operational discipline turns security from a compliance box-tick into something that actually supports the business; a foundation for confidence rather than a source of friction.
Build it in, don’t bolt it on
Modern threats call for an architectural mindset, not a reactive one. Building security into the architecture, the delivery pipeline and day-to-day operations from the start rather than trying to add it in later is what makes the difference between a cloud environment that merely works and one that holds up under real pressure.